Cloud hosted
Tenant-scoped access on HTQLDB’s cloud foundation.
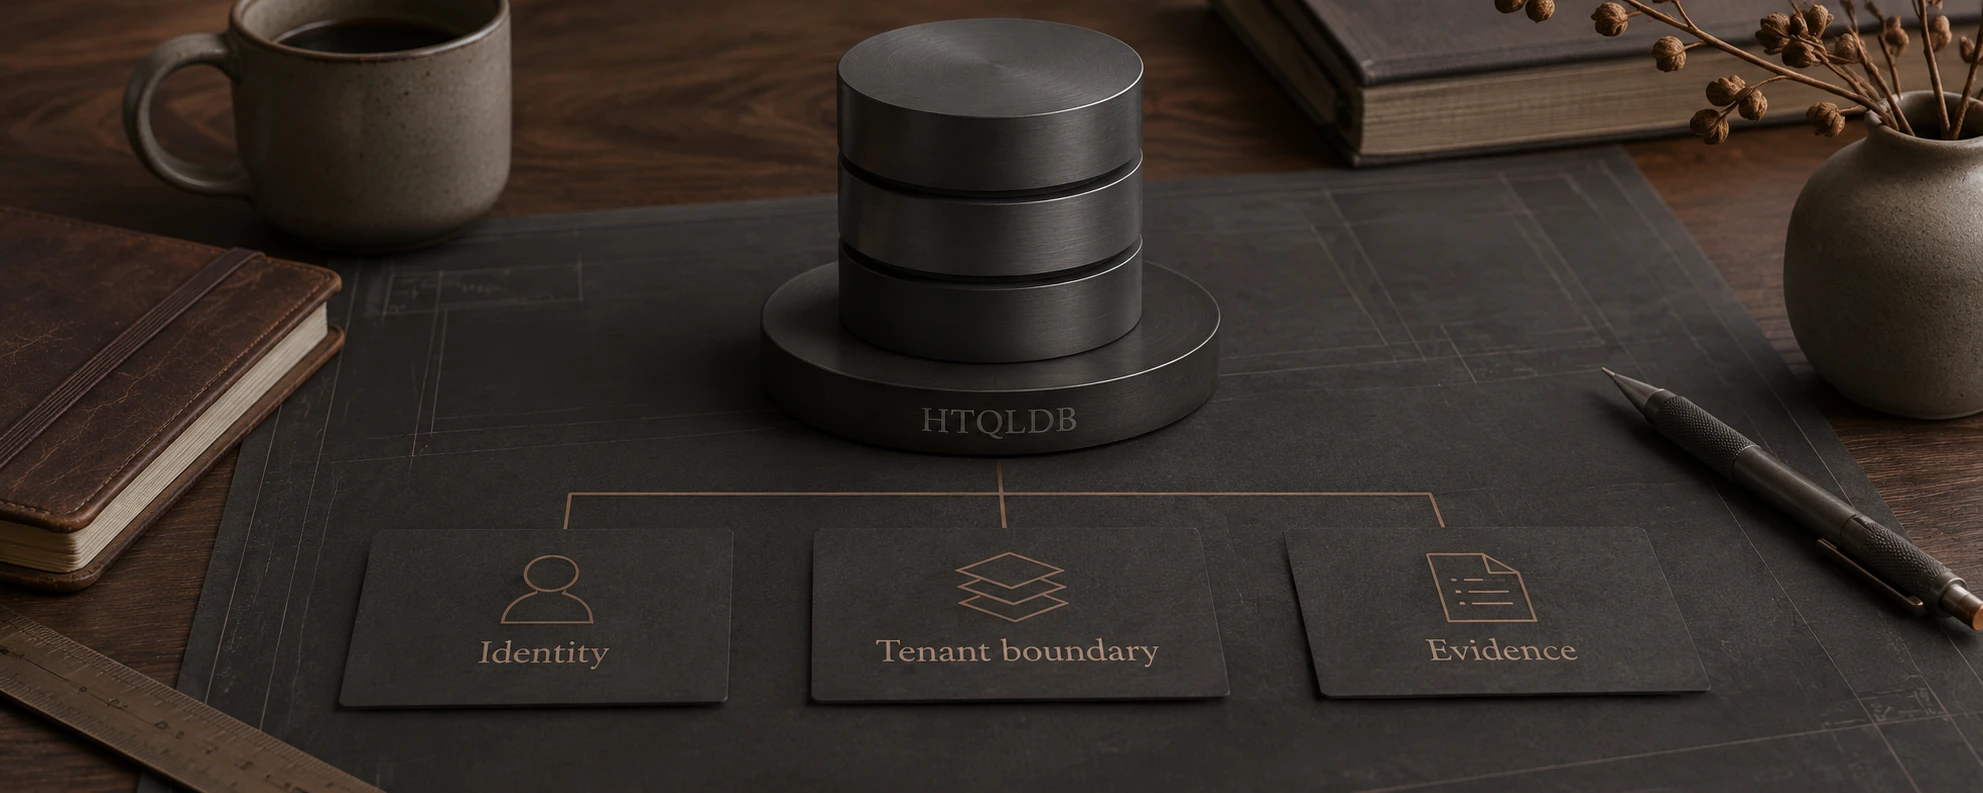
HTQLDB · Trust Ready
Build on a database where identity, permissions, protected data and verifiable records are part of the foundation. Govern access and execution from the very first request.
Trust in every operation
Applications, AI and financial operations share the same underlying data. HTQLDB brings identity, authorisation and evidence into the operations that use it.
Nothing is allowed until it is granted.
Every call passes the access tier. Identity and permissions are checked before the request reaches the database.
PostgreSQL row-level security binds access to the caller’s tenant. Queries, reports and AI operations remain within their authorised data scope.
Own records (row-level security).
Own records (row-level security).
Examples of data classification
Classification controls apply according to the sensitivity of the record.
Encrypted by design
Protected customer data is encrypted.
Blind-index search
Search protected values using blind indexes.
Keys stay protected
Identity service and vault hold the keys, outside the application.
Designed around protected customer data requirements.
Governance, treasury, identity and audit records carry signed evidence. Financial operations and authorisation decisions can be examined against their recorded history.
Signed anchor chain
Tenant-scoped access on HTQLDB’s cloud foundation.
Deploy HTQLDB on your own premises, within your infrastructure and security boundary.
Trusted node communication
The Control Plane manages node identities and mutual TLS for committed HTQL transaction replication.
Bring your application and its security requirements to HTQLDB.